
Workflow scope
Authorize defined workflows while other AI activity remains on the existing provider path.
Unmatched or ambiguous traffic should remain outside Forge intervention rather than expanding authority by assumption.
Customers retain the underlying provider relationship, decide which eligible workflows are in scope and preserve a practical path back to the existing authorized environment.
Control is designed to remain visible in the operating model: what Forge can touch, when it can act, what remains outside scope and how influence can be suspended.
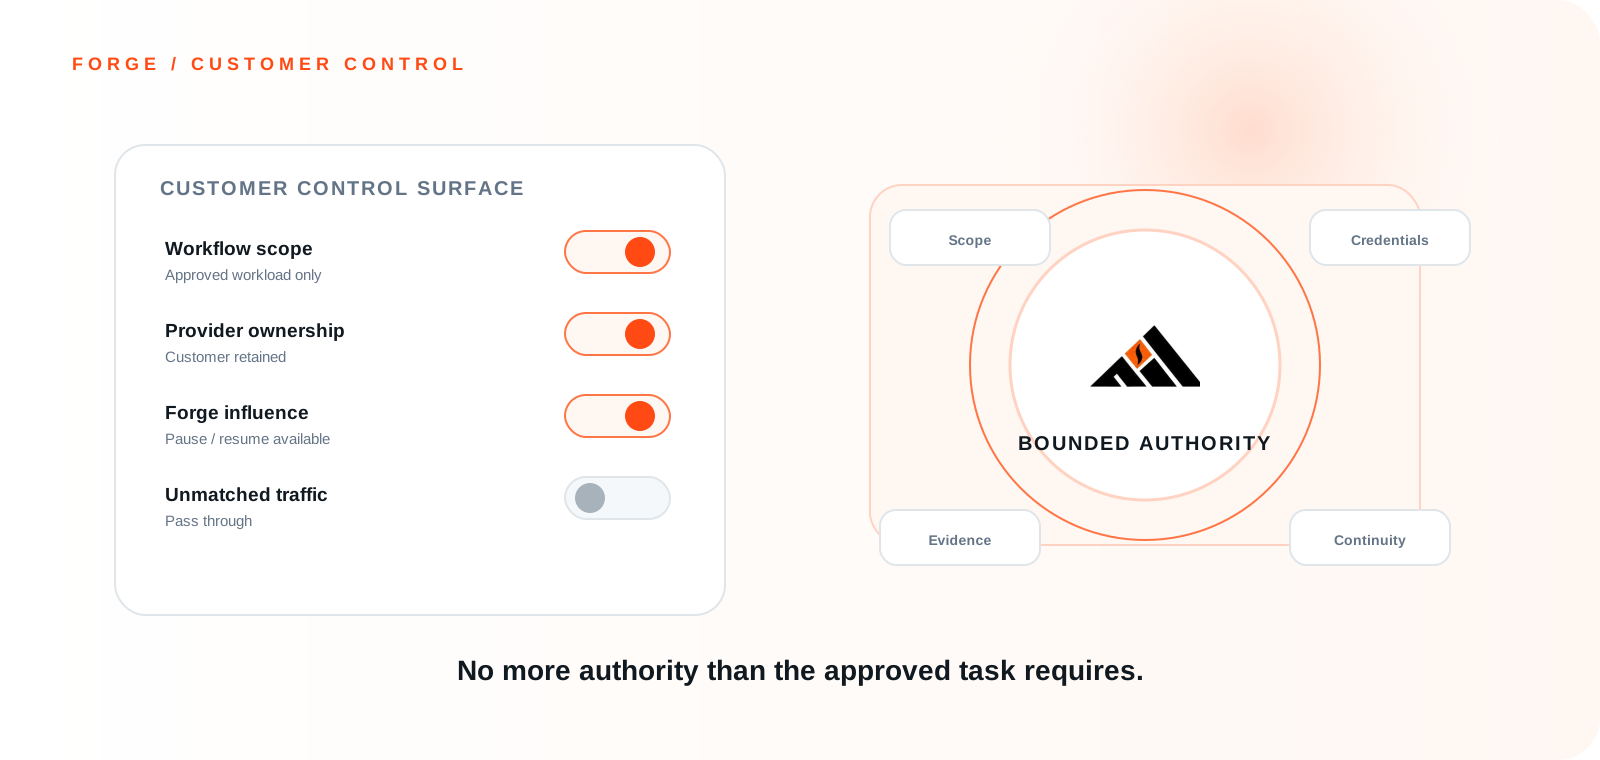
Each control has a practical operating consequence. Scope, provider ownership and pause/resume choices remain explicit so Forge never needs implied authority beyond the approved workload.
Authorize defined workflows while other AI activity remains on the existing provider path.
Unmatched or ambiguous traffic should remain outside Forge intervention rather than expanding authority by assumption.
Keep provider accounts, commercial relationships and billing visibility.
Forge uses customer-scoped approved access rather than pooling customers into one shared provider identity.
Suspend Forge influence when needed.
Continuity configuration can route eligible activity back to the authorized baseline path.
Where approved continuity configuration is in place, the customer can suspend Forge influence and return eligible activity to the existing authorized path.
Start with a high-level qualification conversation. No sensitive or confidential information is required.