
Tenant isolation
How customer identity, authority and access are separated.
Forge can support security review at an appropriate level while protecting proprietary optimization IP and sensitive implementation details.
The diligence objective is to answer the customer’s material security questions clearly while avoiding disclosure that would create unnecessary attack surface or expose protected implementation methods.
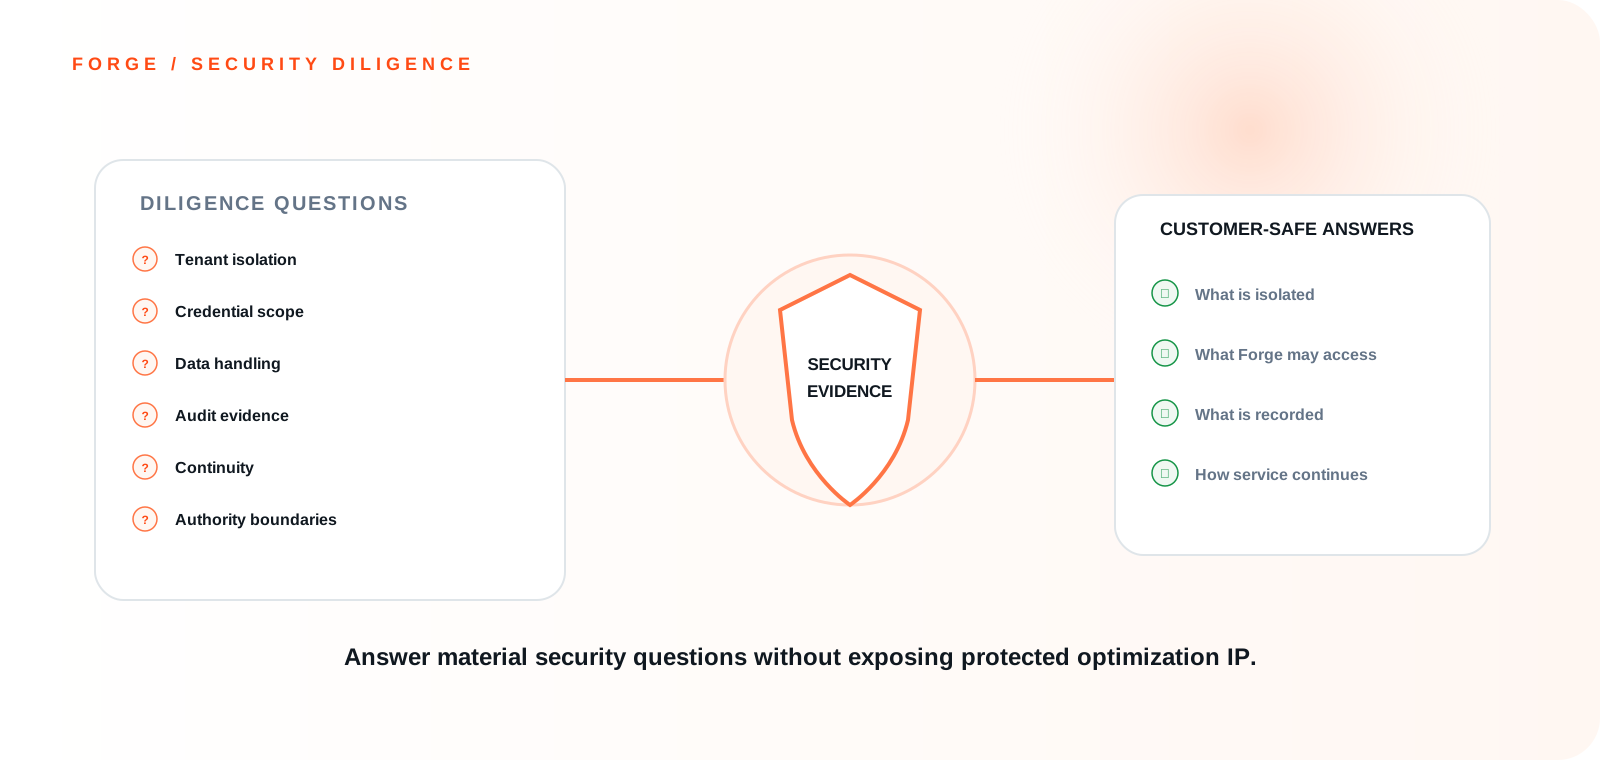
The public site can state the questions Forge is prepared to address during qualification. That includes architecture, data handling, tenant isolation, credential scope, audit evidence, continuity and the boundaries of what Forge is authorized to do.
How customer identity, authority and access are separated.
How provider and context credentials are scoped and protected.
What content is processed, retained, minimized or customer-resident.
How the customer’s existing provider pathway remains available.
What operational and Proof evidence is retained without exposing unnecessary sensitive content.
How customer access and credentials can be revoked or closed.
How material technical changes are governed after activation.
How customer-visible incidents and continuity actions are handled.
Start with a high-level qualification conversation. No sensitive or confidential information is required.